Covert mobile device detection spans passive RF receivers like PocketHound, prison-grade systems like UMDS, and software that hunts hidden spy apps. Here is how the hardware works, what ranges and specs to expect, and where the legal lines fall.
What Is Covert Mobile Device Detection?
Covert portable non-public device identification– unearthing an iPhone hidden, unauthorized or contraband without the phone person knowing they’ve been located. And in my own sweeps, it is never to pull a signal just for ego reasons—it is always three things fast: A device? Which brings us to three separate tool families — first, hardware that sniffs RFE emissions from handsets; second software for hunting hidden spy apps on a phone already within your control; last the legal and enterprise frameworks governing what you're allowed do in whatever you find.
This post is not for the sake of academia but actually falls in line with searcher intent. There is intrigue as to: how the actual detection works, where it reaches, what are those published specs (and maybe even some math) meaning, whether use cases can justify the spend and so on — legal limits. On the hardware side, this consists of two physical principles: radiofrequency (RF) detectors that eavesdrop on uplink cellular transmissions and ferromagnetic sensors closely monitor the magnetic components within a handset. The rest of the stuff in this article is just a riff on those two ideas.
How Do Cell Phone Detectors Work?
High-end and expensive covert cell phone detectors are generally passive high-frequency receivers tuned to cellular uplink bands. They don?¢€œt interfere with, spoof or engage the network?¢€” they simply passively listen for transmissions a phone sends out when it is in standby and during active voice, texting and data sessions then alert the operator via LEDs, vibration or both. The phone and the carrier network have no way of knowing where a detector is because it acts as a passive receiver. That is the essence of what constitutes the hidden value proposition.
The second family of detectors works on an entirely different principle. Ferromagnetic detectors pick up the ferromagnetic materials inside a phone's construction at close range — something RF detectors simply can't do once a handset is powered off, wrapped in foil, or otherwise shielded from radiating. In practice, a thorough sweep relies on both: RF gear to catch live emissions from a distance, and a magnetic detector to confirm a powered-down handset tucked inside a wall cavity, a piece of furniture, or a vehicle panel. Detection range varies a lot depending on which tool you're using — anywhere from a couple of feet for magnetic sensing, up to 150 feet for general consumer phone detectors, while RF detection outdoors can pick up signals as far as a mile away under favorable conditions.
PocketHound Cell Phone Detector: Specs, Range and Covert Alerts
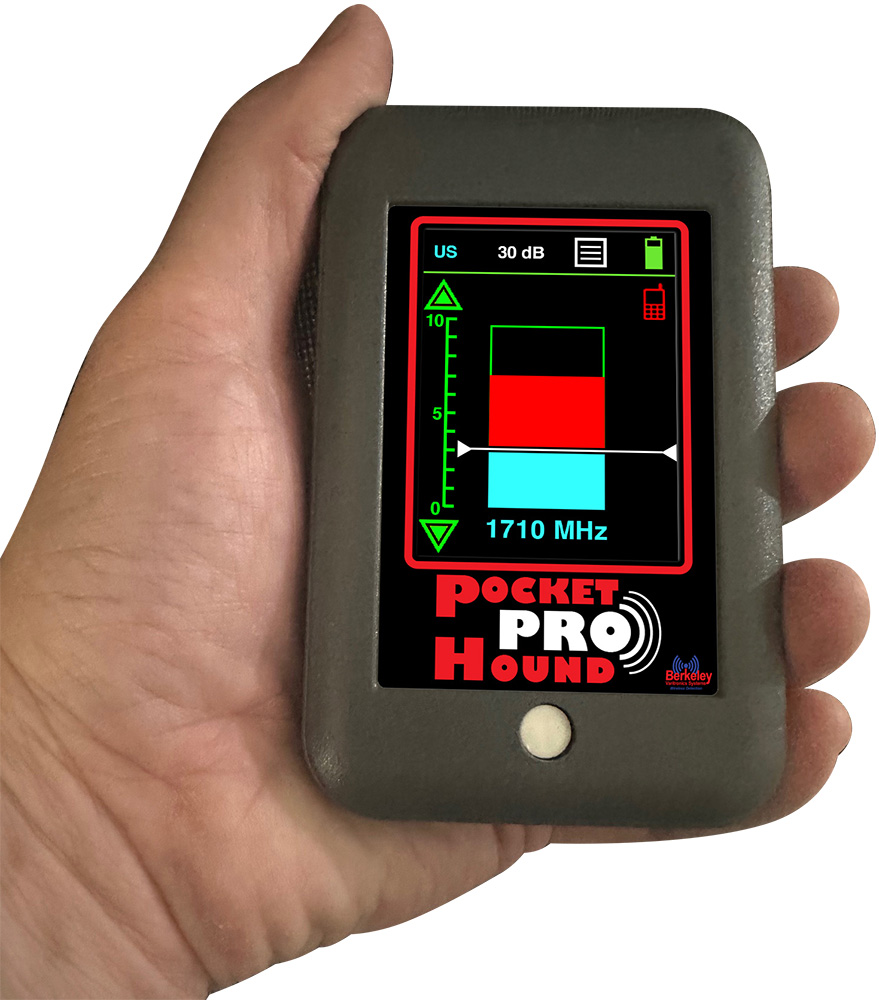
PocketHound by Berkeley Varitronics Systems (BVS) is the archetypal, portable passive receiver. About the size and weight of a deck of cards tuned to 2G, 3G, and their supporting bands: PCS; CDMA/WCDMA (UMTS); GSM; EGSM. The weight is under 1 lb and the overall dimensions are 4 x3x1 inches, Detection range of 75 feet indoors in normal conditions up to roughly 25m.
When you compare the tools, the published performance figures do matter. The PocketHound displays -83 dBm sensitivity, 60dB dynamic range and detector resolution of only 2dB with bandwidth/ selectivity rejection greater than 50db at +1 MHz from the edges of each Uplink band edge for both the GHz bands listed in Table I. Alerts are generated from superbright LEDs plus an internal REED vibrator that is RSSI-sensitive, along with a two position slider switch and auto threshold sensor to detect above ambient RF noise. Internal run time of Li-Ion Polymer battery minimum 2 hours, with an extended battery optional; Mini-USB only to charging.
| Specification | PocketHound |
|---|---|
| Sensitivity | -83 dBm |
| Dynamic range | 60 dB |
| Detector resolution | 2 dB |
| Bandwidth resolution | 4 MHz / 20 MHz |
| Selectivity rejection | >50 dB at 1 MHz from uplink band edges |
| Detection range | Up to 75 ft (about 25 m) indoors, typical conditions |
| Battery runtime | Minimum 2 hours, extended battery optional |
| Size and weight | 4 x 3 x 1 in, under 1 lb |
In the U.S., the PocketHound covers LTE Uplink at 699–716 MHz, 777–787 MHz, 788–798 MHz, 824–849 MHz, and 896–901 MHz, along with AWS Uplink at 1710–1755 MHz, 1850–1910 MHz, and 2305–2315 MHz. International versions are tuned for the EU, Australia, New Zealand, Israel, Canada, Sweden, Brazil, and Japan. As for credentials, it took Platinum at the 2013 GOVERNMENT SECURITY AWARDS from Security Product News and was named a BEST OF WHAT'S NEW 2012 pick by Popular Science. It's made in the USA and comes with a one-year hardware warranty; you can extend that by another year for $95.00. One operational caveat worth knowing: standby registration varies by base station — typically every few minutes, but sometimes stretching to 20 minutes depending on the carrier, distance, and handset maker. So a quiet phone isn't always an absent phone.
UMDS: Prison-Grade Multi-Signal Detection
UMDS, from Unify Business Solutions, is a totally stealth and responsive handheld prison mobile detection device that can rapidly monitor each cell for the location of unauthorized financial activity. Different from a hand-held receiver, it scans 2G3G4 G5 GW-FI and Bluetooth through multiple detectors coordinated by a central server. Instead of one operator monitoring a single wing, the system keeps constant surveillance on an entire facility and cross-matches signals from sensor to sensor.
The feature set is designed for institutional settings: stealthy 100% undetectable installation, tamper-proof hardware, remote self-tests, geolocation mapping and heat-map visualization with real-time alerts and historical downloads; whitelisting of device MAC addresses; custom map interactivity including grid & stack views. Licensing issues are not a concern, Unify declares, as it is "only monitoring" rather than jamming the system and therefore isn't interfering with any licensed spectrum. It is aligned to UK Government and Ministry of Justice standards as well ISO 27001 Frameworks. In a building of many real insiders, whitelisting is the pragmatic detail that makes climbing out from false positives workable.
Counter-Surveillance Kits for Travelers and TSCM Sweeps
For people who need to sweep a hotel room, a boardroom, or a rental apartment rather than a prison wing, the COVERT counter surveillance travel kit from ComSec LLC packages the essentials in one case. It includes an RF detector covering VHF/UHF 50-700 MHz, mobile and wireless 700 MHz to 3 GHz, and microwave and wireless 3-12 GHz, plus a Wi-Fi inspection camera with an Android and iPhone app and a 27.5 inch extension pole for looking above ceiling tiles and behind furniture.
The rest of the kit rounds out a proper bug sweep: a dual-purpose camera detector with a day infrared view finder and a night infrared camera, a key fob and room key Faraday bag to isolate a device you have already found, a 900 lumen LED inspection light with 395 nm UV for spotting residue and markings, and a multi-function USB and Type C tester measuring 3.6V-30V and 0-5.1A. In my experience, the Faraday bag is the piece people forget, and it is the one that stops a recovered phone from continuing to report its location while you decide what to do next.
Detecting Covert Spy Apps on iPhone and Android
Hardware finds hardware, but a phone that is already in your pocket can be compromised by software. Spy apps available in 2025 include mSpy, FlexiSPY, Spyera, XNSpy, uMobix, and eyeZy. Their capabilities include call and message logging, GPS tracking, keystroke capture, screenshots, ambient microphone activation, and social media monitoring. Some require rooting or jailbreaking the target device, while others quietly pull data from iCloud backups without jailbreaking at all, which is why a clean-looking phone is not proof of a clean phone.
On iOS, the Covert Detector: Device & Cam app by developer Beulah Budge detects smartphones, Bluetooth gadgets, and Wi-Fi networks. It is a 29.6 MB download, requires iOS 16.0 or later, offers in-app purchases listed at $8.99, $14.99, and $15.99, includes a 3-day trial, and carries one rating at 5.0. Consumer apps like this are a reasonable first pass for a traveler, but they are not a substitute for a forensic examination when the stakes are legal or corporate. Covert channels on Android and other mobile platforms can exfiltrate data through ordinary network connections or unusual sensors such as light sensors, which makes reliable detection genuinely difficult without endpoint tooling.
Is Covert Mobile Device Data Collection Legal?
It depends on jurisdiction and context, and the answer is never a blanket yes. Covert collections mean discreet acquisition of mobile device data without the subject's awareness or consent. That requires strict legal compliance, ethical review, technical expertise, defensibility of the collected data, and risk management. In practice, investigators lean on alternatives to full device imaging: remote access, live monitoring, network-based collections, and selective extraction of only the specific data a warrant or policy permits.
Enterprise mobile device security runs into the same wall from the other direction. Mobile phishing is the top threat vector, with nearly one in three corporate data breaches starting on a compromised mobile device, yet endpoint detection and response (EDR) typically does not support phones or tablets. Organizations use mobile device management (MDM), identity threat detection and response (ITDR), and mobile security assessment tooling (MSAT) instead. NIST SP 800-124r2, published May 17, 2023, covers mobile device management, mobile application vetting, mobile threat defense, and the mobile-device life cycle for both organization-provided and personally owned devices. A 2013 Office of the Director of National Intelligence report found that out of 39 departments and agencies, 44% fell short of minimum standards for an effective insider threat program, a reminder that policy gaps, not tools, are usually the weakest link.
Matching the Tool to the Job
Choosing between a handheld receiver, a facility-wide system, and a software scan comes down to what you are actually trying to learn. A handheld like PocketHound answers whether a live phone is transmitting in a room, quickly and without infrastructure. A system like UMDS answers where activity is concentrated across a large building, continuously and to cell-level precision. A phone-side app answers whether the device in your own hand has been tampered with. None of the three replaces the others.
The terminology around this field is dense, and knowing it helps when you talk to vendors: covert cell phone detector, passive receiver, TSCM tool, RF detector, ferromagnetic detector, bug sweep, counter surveillance, stalkerware, spyware, covert channel, MDM, EMM, MTD, MAV, ITDR, and MSAT. The organizations and products that come up repeatedly include Berkeley Varitronics Systems, L&G International, Unify Business Solutions, ComSec LLC, Cellbusters, NIST, NSA, Huntress, Purpose Legal, ModeOne, LaSorsa & Associates, ACTi, and IPVM, alongside the consumer spy apps already named. If you take one operational lesson from all of this, it is that detection is a layered discipline: RF for live emissions, magnetics for shielded handsets, software for compromised devices, and documented legal process for everything you intend to use afterward.
What Are the Practical Limits of Covert Detection?
Every tool in this category has a ceiling, and pretending otherwise is how sweeps fail. RF detection depends on a phone actually transmitting, so a handset in airplane mode, powered off, or sealed in a Faraday bag is invisible to a passive receiver. Standby registration timing makes this worse, since a phone may check in only once every few minutes up to 20 minutes. Ferromagnetic detection solves the powered-off case but only at close range, meaning someone still has to physically search the space. Software detection on the phone side struggles with covert channels that hide data in ordinary network traffic or unusual sensors.
The legal ceiling is just as real as the technical one. Covert collection without proper authority creates evidence that is difficult to defend and risks serious liability, which is why the defensibility of collected data belongs in the planning stage rather than the report stage. Budget accordingly too: a handheld receiver, a multi-sensor facility deployment, and a forensic examination sit in completely different price brackets, and the extended warranty line item on a PocketHound, listed at $95.00 for an additional year, is a useful reminder that sustainment costs follow the initial purchase.
Frequently Asked Questions
How do covert cell phone detectors work?
Most are passive RF receivers tuned to cellular uplink bands. They scan for phone transmissions in standby or active voice, text, and data modes, then alert the user with LEDs or vibration. Ferromagnetic detectors instead sense magnetic components inside a phone at close range, which is the only reliable way to find a powered-off or shielded handset.
What is the detection range of a PocketHound cell phone detector?
PocketHound detects nearby cell phones up to 75 feet indoors, roughly 25 meters, under typical conditions. It is a passive receiver with a 60 dB dynamic range, -83 dBm sensitivity, and a built-in omni-directional antenna, and it weighs under one pound at 4 by 3 by 1 inches.
Can UMDS detect 5G and Wi-Fi devices in prisons?
Yes. UMDS coordinates multiple detection points across 2G, 3G, 4G, 5G, Wi-Fi, and Bluetooth via a central server. It provides real-time alerts, heat-map visualization, and cell-level geolocation, and it can whitelist authorized MAC addresses to eliminate false positives from staff devices inside the facility.
Is covert mobile device data collection legal?
It depends on jurisdiction and context. Covert collections require strict legal compliance, ethical review, technical expertise, defensibility of collected data, and risk management. Practitioners typically use remote access, live monitoring, network-based collection, and selective extraction rather than full device imaging, and they document authority before any acquisition begins.