GPS Spoofing Explained: How Fake GPS Signals Work and How to Defend
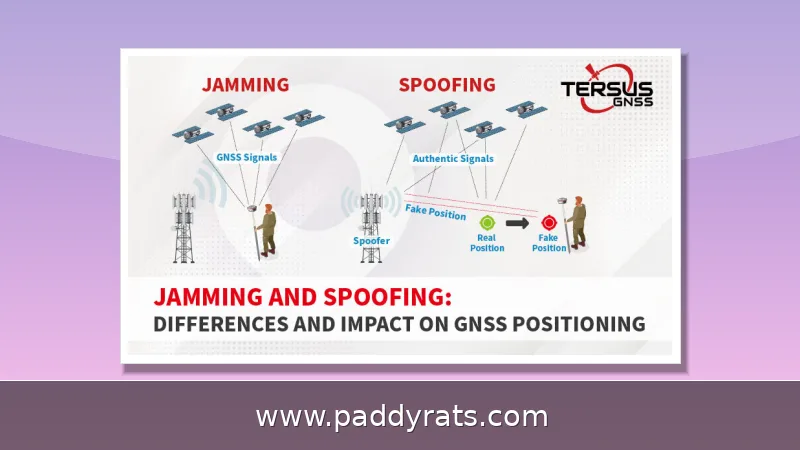
GPS spoofing floods a receiver with counterfeit satellite signals so it reports a location that is not real. Here is how the attack works, how common it has become, and how to detect and defend against it.
What Is GPS Spoofing and How Does It Differ From Jamming?
GPS spoofing, by contrast, is a technique which finds the cause Global Positioning System metadata (e.g. Location Coordinates / Time) via radio transmission of fake-GPS signals attractive misrepresentation to where that receivers grace are actually stationed or measure time. However, a nearby radio transmitter can swamp the faint satellite signals with misinformation in the form of bogus coordinates causing devices, vehicles or apps to indicate they are where their not. This term also extends more broadly to GNSS spoofing, as the same trick is effective against Galileo, GLONASS and BeiDou respectively.
Jamming and spoofing are sometimes spoken of in the same breath, but they are different kinds of attack. If jamming gets through, the GPS receiver cannot even create a location at all because it is drowned out with radio noise. Spoofing is nastier: this pretends to be a Legitimate satellite signals so that the receiver thinks it receiving false data as True. In practice, a spoofing attack can be considered as an enhanced selective jamming where only specific receivers are causing disruption while the neighboring receiving devices work properly.
That distinction is important for anyone defending a system. The fact that a jammed receiver almost always knows something is wrong and thus loses its fix, while the spoofed one may be reporting an utterly false position valid for hours on end is likely responsible. That quiet failure mode is what makes spoofing so scary in aviation and maritime tracking.
How GPS Spoofing Actually Works: Signals, PRN Codes, and SDR Tools
IntroducerAn attacker uses a signal generator or software-defined radio (SDR) to broadcast fake GPS signals stronger than genuine satellite signals. Spoofing signals are approximately 500 times stronger than genuine GNSS, sufficient to drown out the actual constellation at the antenna. Spoofing itself involves sending realistic satellite signals on those same frequencies, usually L1 GPS — at around 1575.42 MHz or so —and that is why a standard receiver can not intuitively distinguish between them easily.
The civilian signal structure is the choke point. The U.S. GPS system has already 31 Navstar satellites, which are issuing PRN codes; although military codes of an equipped satellite will be encrypted and civilian PRN mecoms unencrypted (published in publicly available databases). The hacker identifies which satellites are overhead based on orbit data, synthesizes new codes from the available public PRN codes and transmits them at an incrementally stronger amplitude until a receiver locks onto the fake signals. When the receiver locks onto its target, hacker inputs fake coordinates.
Both are different kind of attack. The faked signals are not time-synchronized with the authentic ones, hence making this form of take-over asynchronous and cruder — it is therefore easier to be detected. The other method is time aligned in which the fake signal correlates with the original one and thus, allowing sliding of receiver without being aware. Both do this using cheap SDR hardware with open-source software and can even scale down to miniaturized handheld devices, that are inexpensive.
Deployment is equally flexible as the hardware. The first option is to place a spoofer in close proximity of the target, passenger take onto an airplane or flown on it via drone. It's one of the reasons spoofing incidents have jumped up so quickly since 2023, as everything that can be done is at a low barrier to entry.
Who Carries Out GPS Spoofing and Why
Motivation varies from the level of State oppression to cheating at mobile games. State actors have been linked to many of the larger clusters of spoofing, especially by researchers and monitoring groups around the globe; however, with nearly 10,000 cases attributed possibly from Russia itself. In those cases, the targets are conventional weapons systems: achieving their goals usually consists of harassing or concealing aircraft and vessel navigation paths or protecting certain sites from drones (US launch outside area) and guided munitions.
The capture of a Lockheed RQ-170 drone in northeastern Iran back in December 2011 was one of the first cases suspected to have been reached with aided navigation data fed into aircraft that, under their own power would not be able to land. That account, whether entirely true or not became the standard for how a spoofing assault might take control of an unmanned vehicle without firing a single shot.
On the civilian front, they are more banal: players wishing to fake a comically location on Pokémon in or escaping regional content blocks like people using those same apps to conceal where they really are. The very existence of so many fake GPS location apps—and the reason why Android comes with its own built-in mock location tools—is that consumer demand.
Real-World Impact: Aviation, Shipping, and Critical Infrastructure
Spoofing is quite visible today with respect to aviation. On September 6, 2024 the WorkGroup final report showed a significantly greater increase in operation than was seen earlier —spoofing for an average of about half that number and on one day reached up to +500% over this pace with nearly2F/-5 (1,285-300 →) ≈1/ ((14+70)) from Q & ↓ f. Nowadays, as many as a dozen spoofing events are detected on any given day via the use of ADS-B reports from aircraft and GPSwise alone processes over 250 million ADS-B messages every single day to plot them.
When an aircraft's GPS is spoofed, the position feed can jump to a wrong location, which corrupts ADS-B broadcasts, flight tracking, and any system that trusts GPS time. Pilots still have inertial and ground-based backups, but the workload spikes and the risk of confusion rises. The same problem hits shipping, where a wrong fix near a coastline is far more than an inconvenience.
Critical infrastructure depends on GPS for timing as much as for position. Power grids, telecom networks, and financial timestamping all lean on satellite time, so an extended spoofing campaign can ripple well beyond navigation. Companies such as CRFS, Septentrio, Swift Navigation, NextNav, and Incognia build receivers and location technology specifically aimed at holding up under interference, which tells you how seriously the industry treats the threat.
GPS Spoofing Statistics and Incident Trends
The headline numbers are stark, and they come from monitoring networks rather than one-off anecdotes. Spoofing attacks have become increasingly common since 2023, and the daily flight counts above show how fast the curve bent. Because these figures come from crowd-sourced ADS-B data, they are a floor rather than a ceiling; incidents over water or in low-traffic airspace are easy to miss.
A few data points are worth keeping in mind when you read about this topic, so here is a quick reference table.
| Metric | Figure | Source / Period |
|---|---|---|
| Increase in spoofing | 500% | WorkGroup final report, Sep 6, 2024 |
| Flights spoofed per day | ~1,500 vs. 300 | WorkGroup, 2024 vs. Q1/Q2 2024 |
| Attributed Russian cases | Nearly 10,000 | Monitoring group estimates |
| Spoofed signal strength vs. authentic GNSS | Up to 500x | Technical analyses |
| ADS-B messages analyzed daily | 250 million+ | GPSwise |
Those numbers explain why live interference maps from Flightradar24 and GPSwise have become standard tools for analysts. They also explain why the question of whether GPS spoofing is illegal keeps coming up: in the United States, transmitting interfering signals is generally unlawful, but enforcement against foreign state actors is a diplomatic problem, not a technical one.
How to Detect GPS Spoofing: Signal, Timing, and Cryptographic Methods
Detection methods include signal strength monitoring, time-of-arrival analysis, and angle-of-arrival analysis with antenna arrays. A sudden jump in received power on L1, or a signal that arrives from the wrong direction, is a strong hint that something is wrong. Cross-correlating multiple GNSS systems such as GPS, GLONASS, BeiDou, and Galileo helps too, because a spoofer rarely fakes all constellations consistently.
Crowd-sourced receiver data adds another layer. When hundreds of aircraft or phones in the same area report impossible positions or timing anomalies at once, that pattern is far more convincing than any single receiver's alarm. This is the approach behind public jamming and spoofing maps, and it is how most real-world incidents get noticed in the first place.
The strongest long-term answer is cryptographic authentication, such as Galileo PRS and GPS III signals, which make it much harder to forge a believable transmission. Anti-spoofing research from groups like the Stanford GPS Lab, with FAA support, has pushed much of this work forward. Until authenticated signals are everywhere, defense is a layered mix of signal checks, timing checks, and plain operational skepticism about any single source of position data.
How Can You Spoof Your Own Location, and Is It Legal?
On Android, apps that spoof location without root must use the built-in Mock Location API in Developer Options. On Android 6.0 and above you select the specific app in Developer Options; older versions use a simple checkbox. The Mock Location API asks for five variables: latitude, longitude, altitude, speed, and accuracy. Most spoofing apps only change latitude and longitude, leaving altitude, speed, and accuracy at constant values such as 0, 1, or random.
That shortcut is exactly what detection systems look for. Real GPS values fluctuate every second when you are moving and even when you are standing still, and movement never travels in a perfect straight line. GPS JoyStick is often described as the only app in the Google Play Store that mocks realistic, always-updating data for all the necessary GPS values, with customizable settings, favorites, routes for teleporting and automated walking, and a teleport dialog for entering latitude and longitude.
A VPN is a simpler option for some use cases. You subscribe, install the app, log in, connect to a server in another country, and optionally enable location spoofing in the browser extension or GPS override on Android. NordVPN offers over 9,300 servers in 211 locations with unlimited data, no logs, and a 30-day refund; Surfshark offers unlimited simultaneous connections and an Override GPS Location toggle in Advanced Settings, with Surfshark Starter at $1.78 per month.
Dedicated tools go further. iMyFone AnyTo supports iOS 26 with no jailbreak or root, and offers multiple movement modes including simulated walking, teleport, and a joystick, plus walking speed, pauses, and looped routes. PGSharp is Android only, installs via APK, and adds a virtual joystick, instant teleport, auto-hatching, and PokéStop spinning. iPOGO is iOS only, needs a signing service or third-party tool, and can get revoked. Here is how the popular options compare.
| Tool | Platform | Strengths | Weaknesses |
|---|---|---|---|
| iMyFone AnyTo | iOS / Android | Low ban risk, very high stability, free trial | Some advanced features are premium only |
| PGSharp | Android only | Easy setup, free version available | Medium-to-high ban risk, movement not very realistic |
| iPOGO | iOS only | Auto catch, auto spin, map radar, Shiny scanner | Tricky install, easier for Niantic to detect, unstable long term |
| Surfshark | Cross-platform | Unlimited connections, GPS override setting | Coarser location control than dedicated spoofers |
Legality is where this gets serious. In the United States, transmitting a signal that interferes with GPS is generally prohibited, and using a spoofed location to commit fraud or violate a platform's terms can carry separate penalties. For consumer apps, the practical risk is usually a ban rather than a courtroom. For anything touching aircraft, ships, or critical infrastructure, spoofing is a criminal matter and a national security concern. Nothing here is legal advice, and this article is not investment advice either.
How Do You Defend Against GPS Spoofing and Jamming?
Defense starts with not trusting a single source. Combine GPS with inertial navigation, barometric altitude, and terrestrial timing references so a spoofed fix has to beat several independent measurements at once. Aviation and maritime operators should also train crews to recognize the warning signs: a position that drifts without matching the instruments, timing errors, or ADS-B reports that other aircraft say are wrong.
For developers and product teams, validate the data your app receives. Check whether altitude, speed, and accuracy values look physically plausible, watch for coordinates that never fluctuate, and flag impossible jumps in position. Incognia and similar vendors sell spoof-resistant location technology for exactly this purpose, and Android's own mock location flags can be read by apps that care about integrity.
On the infrastructure side, holdover modules and hardened receivers from vendors like CRFS and Septentrio keep timing stable when the sky goes bad. The realistic goal is not perfect immunity but graceful degradation: know when you are being attacked, keep operating on backups, and log enough evidence to attribute the event later. That layered posture is what separates a nuisance incident from a real outage.
Frequently Asked Questions About GPS Spoofing
Frequently Asked Questions About GPS Spoofing
What is GPS spoofing in simple terms?
GPS spoofing is a technique that manipulates Global Positioning System data by broadcasting counterfeit GPS signals, misleading a receiver about its actual location or time. A nearby radio transmitter overrides weak satellite signals with false coordinates, so devices, vehicles, or apps report a position that is not real.
How does GPS spoofing actually work?
An attacker uses a signal generator or software-defined radio to broadcast fake GPS signals stronger than genuine satellite signals. The receiver locks onto the spoofed codes, then the attacker feeds false coordinates. Civilian PRN codes are unencrypted and public, which makes receivers vulnerable to this kind of override.
What is the difference between GPS jamming and spoofing?
Jamming drowns out GPS signals with radio noise, so the receiver simply cannot produce a location. Spoofing is more insidious: it mimics genuine satellite transmissions so the receiver believes false information is real. Spoofing can function as a targeted form of jamming that only affects specific receivers.
How can GPS spoofing be detected?
Detection methods include signal strength monitoring, time-of-arrival analysis, angle-of-arrival analysis with antenna arrays, cross-correlating multiple GNSS systems like GPS, GLONASS, BeiDou and Galileo, crowd-sourced receiver data, and cryptographic authentication such as Galileo PRS and GPS III signals.