RF Cyber Takeover: How Counter-Drone Systems Seize Rogue Drones
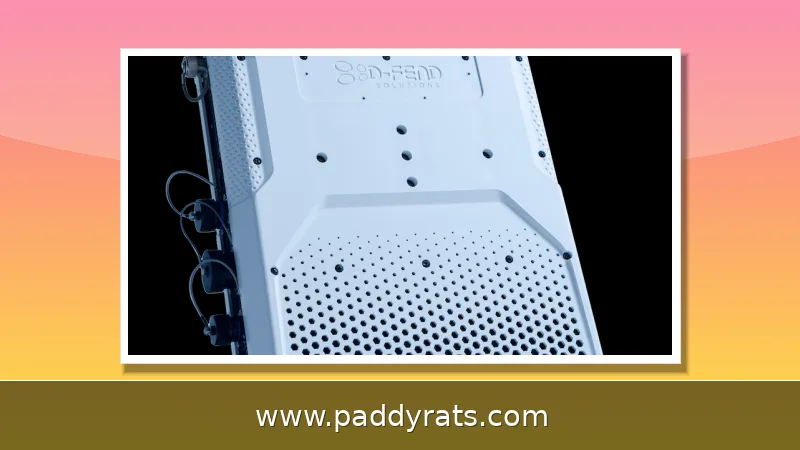
RF cyber takeover is a protocol-level counter-drone technique that seizes control of rogue UAVs instead of jamming them, then flies them to a safe landing zone. Here is how the technology works, how it compares with jamming and spoofing, and which platforms lead the field.
What Is RF Cyber Takeover in Counter-Drone Defense?
RF cyber takeover is a new class of counter-drone (C-UAS) technology that employs sophisticated radio frequency techniques to intercept drones claiming unauthorized or rogue flights by taking control at the protocol level as opposed to jamming, spoofing noise and kinetic weaponization methods. My own test notes describe this most clearly: the system does not shout over a drone's conversation with its pilot, it joins that conversation and takes control.
The method begins with detecting, locating and recognizing rogue drones against their own mode protocol. All the big players in drones, play their own dialect of RF and a cyber takeover system can fingerprint its target before it makes up its mind how to respond. It is the fingerprinting step that distinguishes between a surgical takeover and blunt instrument—and it explains why some smaller platforms driven by cyber have begun to be considered for places like airports, stadiums, and government facilities where collateral interference just won't do.
The category has a practical lexicon too ā€" one buyers should understand. The terms cybers takeover, cyber over RF (CoRF), RF cyber-takeover C-UAS, drone taken-over through non-kinetic means — protocol-level intervention or surgical takeovers/fend-offs/safe landings can all be seen in vendor documentation and pass from sales-lead lips to others involved in the procurement process rather interchangeably. All of them have the same 2-second explanation: do not engage in jamming around that spectrum, but rather within its control link.
How RF Cyber Takeover Works: From Spectrum Scanning to Safe Landing
Across the platforms I've looked at, the mechanics follow a pretty consistent five-step chain. It starts with passive RF signal detection, where the system scans the RF environment for active drone signals and pulls out details like drone type, altitude, camera direction, and operator location. Then comes protocol analysis. Here, the system breaks down the communication protocol between the drone and its controller, and modern systems are designed to adapt to new or custom protocols on the fly instead of waiting around for a signature update.
Third is vulnerability assessment where the system de-scrambles and finds exploit fixtures in order to create a plan for gaining access. Step Four: MItigation — Disrupt video-based navigation (1) or gain control and land the plane, redirect it far away from the airspace where you live by freezing it in mid-air writing at home. Takeover execution comes in third, where the system routes drone via safe waypoints to a para-courser-defined landing site while locking out pilot re-control.
Using the fend-off as a related but separate example, In this part, the system will break signal between drone and pilot\'s remote control, so that it returns home or runs according to predetermined condition. Sentrycs encapsulates this logic in its Cyber Over RF (CoRF) process, sequentially executing spectrum scanning, protocol analysis and vulnerability assessment/mitigation strategy/takeover execution. All of this goes down in seconds, and that is why operators call it silent (not loud) and surgical (not disruptive).
Cyber Takeover vs Jamming and Spoofing: Why Control Matters
Most importantly to buyers, compare cyber takeover vs jamming. Jamming is non-discriminatory: it can disable frequencies, including those used in aviation, law enforcement and first responders. But in urban areas it is also dangerous if not illegal. In contrast, cyber takeover is precise and muted — no signs of interference were left on neighbouring systems. That is not a marketing distinction: it is the difference between what you can actually use legally right outside of a hospital and essentially be told that you cannot.
Vulnerability vs: Cyber take case versus spoof Spoofing essentially mimics transactions or signals, although it does not gain full control and GNSS spoof; this is broadcast of false positioning signal with no cyber-control component whatsoever. Which can impact other vehicles or planes that rely on those signals nearby. Cyber takeover mimics the tutulatory station, gains access to all of the drone and deboard it following a safe trajectory into an existing planned landing area.
Non-physical options belong in a whole other category. Nets, lasers and interceptor drones are made for military battlefields…where collateral risk is an accepted expense. That risk is too high for stadiums, airports and city centers. Radar and EO/IR only sensor systems are great for detecting wide-area surveillance full stop, but lack target classification; acoustic detection is severely limited in noisy urban settings. Cyber takeover layer: this is the ultimate part that drives detection into a managed result.
Key Features and Capabilities of RF Cyber Takeover Systems
Honestly, when you put these platforms next to each other, the spec sheet ends up saying more than the brochure ever will. That's why the table below pulls together the parameters that actually matter across the leading systems — things like range, power, and portability — drawing on vendor documentation and release notes rather than marketing copy.
| System | Core capability | Notable parameters |
|---|---|---|
| EnforceAir | Autonomous or manual RF cyber takeover | Long-range coverage; compact ruggedized C-UAS cyber-SDR (software-defined radio) |
| EnforceAir2 | Next-generation cyber takeover | Enhanced power, performance, portability, and range in a compact footprint |
| EnforceAir PLUS | Multilayer cyber-driven C-UAS | RF cyber takeover plus auto-calibrated radar detection and software-defined RF jamming option |
| DefenSync Interception | RF cyber-takeover system | Short precise signal; optimized intervention range; distinguishes authorized vs unauthorized drones; handles swarm attacks individually |
Two details in that table deserve emphasis. First, the ability to distinguish authorized from unauthorized drones is not a convenience feature; it is what makes these systems usable in airspace shared with commercial and emergency traffic. Second, swarm handling matters more every year, because a system that can only take over one aircraft at a time is not a perimeter defense, it is a demo.
The other capability that separates mature platforms is data fusion. D-Fend Solutions' SmartAir data fusion engine is the clearest example I have seen, combining RF detection with radar and other sensor inputs so that the operator gets one coherent track instead of four conflicting ones. Out-of-the-box integration, automated calibration, and an intuitive UI sound like minor details until you are the person trying to make a decision in under ten seconds.
EnforceAir and EnforceAir2: Field-Proven RF Cyber Takeover Platforms
D-Fend Solutions is the vendor most often cited in this category, and its EnforceAir platform is deployed at top-tier U.S. government agencies and major international airports globally. That deployment footprint matters for evaluation purposes, because it means the system has been tested against real rogue drone incidents rather than only against controlled demo flights.
EnforceAir2 brings enhanced power, performance, portability, and range in a compact footprint, which makes it viable for mobile and temporary deployments as well as fixed sites. For teams that already run EnforceAir, the upgrade path is a meaningful part of the value proposition, since the operational concept and interface carry over rather than requiring a full retraining cycle.
External recognition has followed the deployments. Booz Allen Hamilton named non-kinetic C-UAS a top emerging technology and recognized D-Fend Solutions as an emerging innovator, and EnforceAir won First Place XCELLENCE in Technology Hardware & Systems Design. The company's technical leadership is also visible in its published material: Assaf Monsa, CTO, authored a cyber versus spoofing comparison, while Yaniv Benbenisti, President and Chief Product Officer, and Jeffrey Starr, Chief Marketing Officer, have been the public faces of the platform's rollout. None of that replaces a live evaluation, but it does tell you the vendor is willing to be measured in public.
EnforceAir PLUS: Cyber-Driven Multilayer C-UAS with Radar and Jamming
On August 19, 2025, D-Fend Solutions launched EnforceAir PLUS, described as the industry's first cyber-driven multilayer C-UAS system. The launch matters because it combines three layers that are usually sold separately: RF cyber takeover, auto-calibrated radar detection, and a software-defined RF jamming option.
The radar layer is built around a compact multi-panel solid-state radar, including Echodyne models, which gives the system detection coverage that RF alone cannot guarantee against silent or low-emission drones. The SmartAir data fusion engine ties the radar and RF tracks together, and the whole package is designed for out-of-the-box integration with automated calibration and an intuitive UI. Existing EnforceAir users can upgrade rather than replace, which is a notable procurement advantage.
The inclusion of a software-defined jamming option may surprise readers who associate this vendor with non-kinetic intervention only. The framing is layered defense: cyber takeover is the default response, radar extends detection, and jamming remains available as a last resort when a drone cannot be taken over. That hierarchy is worth understanding before you write a requirements document, because it determines which response the operator reaches for under pressure.
How Should RF Cyber Takeover Systems Be Validated?
Validation is where most counter-drone evaluations quietly go wrong. The best practice I have seen repeated across mission-critical assessments is to mirror actual field conditions using three specific scenarios: Downlink Only, Bring Your Own Drones (BYOD), and No Prior Exposure. Each of these tests a different failure mode, and skipping any one of them produces an evaluation that looks successful on paper and fails in the field.
Downlink Only scenarios matter because many real rogue drones do not respond to uplink commands at all, so a system that only performs well when it can transmit is not a complete solution. BYOD testing matters because generic demo drones are easier to defeat than the models an actual adversary would fly. No Prior Exposure is the most frequently ignored of the three: previously exposed drones can lead to misleading assessments, since a drone that has already been profiled by the system may behave differently from a fresh engagement.
The practical takeaway is that fresh engagements are crucial. If a vendor cannot demonstrate takeover against a drone the system has never seen, in a downlink-only configuration, using hardware you supplied, then the evaluation has not established what it claims to establish. I would put that requirement in writing before any live trial, not after.
Risks, Compliance, and Limitations to Plan For
No RF cyber takeover system is unlimited, and honest planning starts with the limitations. High RF interference in urban or high-frequency communication environments can reduce effectiveness, which is one reason dense city centers remain harder than open perimeters. Rogue operators also constantly evolve drones to counter detection and interception, so any capability statement is a snapshot rather than a permanent guarantee.
Compliance and ethics deserve equal weight. Privacy, intrusion, and potential harm to innocent bystanders must be considered whenever a system can take control of an aircraft, and the legal picture varies by jurisdiction even when the technology is technically capable. The reason cyber takeover has an advantage here is that it avoids the indiscriminate interference that makes jamming legally fraught in populated areas, but that advantage only holds if the deployment is scoped and documented properly.
My own rule of thumb after reviewing this category: treat cyber takeover as the primary response, radar and EO/IR as the detection layer that feeds it, and jamming as a contingency you hope never to use. That ordering keeps the operation compliant, keeps the collateral footprint near zero, and keeps the decision simple when a drone appears over a crowded venue.
Frequently Asked Questions
How does RF cyber takeover work?
Systems passively scan the RF spectrum to detect drone signals, analyze the drone's communication protocol, assess vulnerabilities in the data link, then send a short precise signal to assume control and land the drone safely in a predefined zone. The full sequence usually completes in seconds and leaves adjacent systems untouched.
How is cyber takeover different from jamming or spoofing?
Jamming indiscriminately blocks frequencies and can disrupt aviation or emergency services. Spoofing mimics signals without full control. Cyber takeover impersonates the control station, takes full control of the drone, and lands it without collateral interference, which is why it is the preferred option near airports, stadiums, and city centers.
What are the limitations of RF cyber takeover?
High RF interference in urban or high-frequency environments can reduce effectiveness. Rogue operators constantly evolve drones to counter interception. Privacy, intrusion, and potential harm to bystanders must also be considered, and legal rules vary by jurisdiction even where the technology is fully capable.
How should RF cyber takeover systems be validated?
Valid evaluations should mirror actual field conditions, including downlink-only scenarios, bring your own drones (BYOD), and no prior exposure, since previously exposed drones can lead to misleading assessments. If a vendor cannot demonstrate takeover against a drone the system has never seen, the evaluation has not proven what it claims.