Whitelist vs Blacklist Spectrum Control: Access Control Approaches Explained
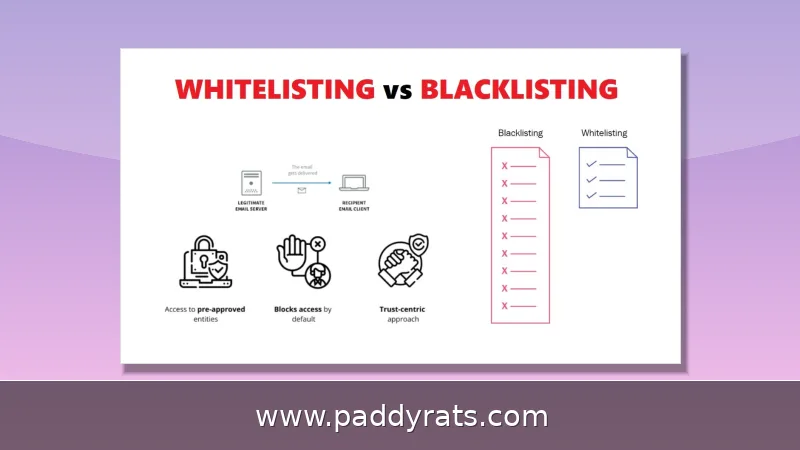
Whitelist vs blacklist spectrum control spans two opposite access control models: default-deny allowlists and default-allow blocklists, with greylisting as the middle ground. Here is how each approach works, where it fits, and how to choose.
What Is the Access Control Spectrum?
World Access Control Day: Access control is seldom an either-or question. In reality, each policy exists on a scale from strict default-deny to slightly relaxed default-allow. On the extreme end, allowlisting (or whitelisting) denies everything unless an entity has explicitly been granted approval. On the flipside, blocklisting (blacklist) allows everything unless a particular entity has been explicitly banned. Greylisting is a bit like where the treasure goes in between (you have an unknown or possibly dangerous source but its held as quarantine so somebody reviews it). Blocklisting and allowlisting are two sides of the same access control coin, a fact noted by application security vendor Binadox in September 2024 which is why they run both with fairly equal frequency rather than choosing one over the other.
The only relevant detail in the way spectrum is framed and mobilized, of course, though it doesn't seem that simple: buy side vs sell side right. Policies nearer protecting default-deny have a smaller attack surface, but great administrative weight. The more default-allow it sits, the less day-to-day workload and bigger attack surface for unknowns. I have seen teams oscillate between the two tails after a single event and its conformable : an incident drives them to allowlist, operational friction brings them back. The question, not which model is better in the abstract but rather which position on that spectrum more closely conforms to the asset you aim to protect.
←Terminology also changes between vendors and standards. That is the default-deny end of allowlist, approved list, inclusion strategy and it can go on to mention zero trust. Default-allow end is described by blocklist, denylist and exclusion strategy. While the middle is characterized by greylist, quarantine and adaptive filtering. Layered defence and defence-in-depth means that you often will stack several positions along the spectrum so a failure in one layer does not become an overall catastrophic collapse.
How Does Whitelisting Work?
Whitelisting, now better known as allowlisting: permission has a default deny model — everything is denied unless explicitly allowed. This was clearly defined in February 2024 by the cybersecurity vendor Instasafe, and its operational logic is simple. You first define the acceptable entities when establishing policy, which can be IP addresses, applications, user accounts or domains. You turn that list into a policy. You then build the policy into the systems that enforce it, by marking any request which is not an approved entry as a denial (by default). The canonical reference for implementing this model at the application layer is NIST SP 800-167, A. Sedgewick et al., 2015; Guide to Application Whitelisting
Implementation follows three broad steps. First, you need to know what is actually permitted to run in your environment based on a security policy defining approved entities. The second step is creating the allowlist itself, considering hashes for applications so that even a modified binary doesn't obtain inherited trust. Third, put it in to firewalls, endpoint agents and mail gateways or application control platforms so that enforcement starts automatically. Allowlists are relatively small and rigid in their nature compared to a blocklist, which means that they can be more easily audited than exhaustive lists of banned items; however, allowlists require rigorous tracking of both assets and users. The effectiveness of an allowlist relies solely upon the strength of its underlying inventory.
The security payoff is real. Allowlisting is proactive because unknown threats are blocked by default; they have no entry on the list. The costs are equally real. The new tools for legitimate change may never come or will be too flexible, traditional rules can hamper productivity (via) full implementation. A more subtle risk is that a compromised approved entity retains access: the list grants permission to an identity, not its current behaviour.
How Does Blacklisting Work?
Blocklisting (formerly blacklisting), which refers to a model of blocking everything unless it has been explicitly allowed In a blog post from February 2024, Instasafe framed the contrast similarly. You identify and enumerate known bad actors — malicious IP addresses, malware signatures, spam domains or abusive accounts — and you plug that enumeration into firewalls, email filters, antivirus engines or content platforms. Everything passes but matching traffic is blocked. Setting it up usually takes less time, and this model requires significantly fewer resources compared to maintaining a granular allowlist.
blocklisting is reactive in itself, which means: The downside It can only block what someone already knows, so it provides incomplete protection against unknown threats and zero-day attacks. If just one entry is missed, it can lead to a breach; the list also needs to be updated regularly because attackers rotate infrastructure. The problem is that too aggressive blocklist tools damage those legitimate sources themselves, by mistakenly trying to flag them as ones of concern. As noted by SiteGround in September 2026, a single listing on a major blocklist like Spamhaus can impact deliverability to thousands of inboxes at once (a useful reminder that these lists wield enormous power over any and all who consult them).
The table below breaks down how the two ends of the spectrum actually differ in practice. It's based on a head-to-head comparison that the YouTube parental control app WhitelistVideo published back in December 2025.
Whitelisting vs Blacklisting: Pros and Cons Compared
Here's a side-by-side look at the two models, compared on the points that actually matter when you're deciding where to land on the access control spectrum.
| Dimension | Whitelist (allowlist) | Blacklist (blocklist) |
|---|---|---|
| Default state | Blocked | Allowed |
| Security model | Proactive | Reactive |
| New content | Blocked until approved | Open until flagged |
| Bypass risk | Very low | High (VPNs, Incognito) |
| Ongoing effort | Moderate curation | Low, set-and-forget |
| False positives | Rare | Common |
| False negatives | Effectively impossible | Common |
| Best for | Young kids, high-security homes | Older teens, open environments |
Read the table as a trade-off curve rather than a scorecard. Whitelisting wins on security, predictability, and false-positive control, but it costs administrative attention and can constrain legitimate activity. Blacklisting wins on simplicity and low friction, but it leaks unknown threats and depends on somebody else maintaining an accurate list. The false-negative row is the one I would highlight: with an allowlist, an unknown threat simply cannot get through the default-deny gate, while with a blocklist the same threat passes silently until someone notices and adds it.
My own rule of thumb after running both models is to match the position on the spectrum to the cost of a mistake. Where a single compromise is catastrophic and the set of legitimate activity is small, allowlisting earns its overhead. Where the legitimate set is enormous and constantly changing, blocklisting plus monitoring is often the only workable starting point, with allowlisting layered on top for the highest-value assets.
What Is Greylisting and Where Does It Fit?
Greylisting offers the middle ground on the spectrum. Instead of immediately allowing or denying, it temporarily quarantines sources that appear suspicious or unknown. Once a human or automated review classifies the source, it moves to either the allowlist or the blocklist. As the email security guide Mutant Mail describes it, the default for greylisting is to quarantine first, which buys investigation time before a final access decision is made. That delay is the entire point: it converts a binary decision into a reviewable one.
Email filtering is where greylisting is most familiar. A mail server can temporarily reject a message from an unrecognized sender and ask it to retry, which legitimate mail servers do and most bulk spam operations do not. The approach filters a large volume of junk with very little configuration, and it composes well with the other two models. In application security, the same pattern appears as sandboxing or manual review queues for unsigned binaries. In network access, it appears as limited-access guest segments that require sponsorship before full access is granted.
Greylisting is not a permanent state, and treating it as one is a common mistake. A quarantine queue that nobody reviews becomes a slow-motion blocklist with extra steps. The model only works when there is a clear owner, a defined review window, and a documented path to either the allowlist or the blocklist. Used that way, it is the most flexible position on the spectrum and the easiest one to defend to stakeholders who object to hard denials.
Whitelist vs Blacklist in Application Security
In application security, the two models show up in different layers. Application allowlisting, the subject of NIST SP 800-167, restricts endpoints to a defined set of approved executables and hashes, which is why it is favored for kiosks, industrial control systems, and high-value servers where the software inventory is stable. Application blocklisting shows up in antivirus signature databases and endpoint detection tools, where the set of legitimate software is too large and too dynamic to enumerate. Most mature environments run both: allowlisting on the critical tier, blocklisting everywhere else.
Network access follows a similar split. Firewalls commonly enforce IP allowlists for administrative interfaces and IP blocklists for known hostile ranges. Huawei's WLAN documentation, updated in June 2026, describes STA blacklist and whitelist configuration for wireless clients, which is a good illustration of how the same spectrum appears inside a single device. Email is the third major arena. Gmail Postmaster Tools and Microsoft SNDS both serve as reputation dashboards that senders consult before requesting an allowlist entry, and SPF plus DKIM authentication is normally a prerequisite for that request.
The practical lesson from all three arenas is that the spectrum is a design tool, not a doctrine. Allowlisting gives you the strongest guarantee at the highest maintenance cost. Blocklisting gives you broad coverage at the cost of unknown-threat exposure. Greylisting gives you a review buffer that keeps binary decisions from being made too early. Choosing deliberately, layer by layer, beats picking one model and applying it everywhere.
How Do You Implement Each Approach?
Allowlist implementation starts with the security policy, not the tool. Define which entities are approved, based on what the system actually needs to do. Compile the list, including hashes or certificates where identity can be spoofed. Then integrate it into the enforcing systems through configuration, and test the deny path before you rely on it. For email specifically, the sequence matters: register your sending IP with Microsoft SNDS, monitor reputation in Gmail Postmaster Tools, and configure SPF and DKIM authentication before submitting any allowlist request to a recipient.
Blocklist implementation is faster but never finished. Enumerate the known dangerous actors you can identify from threat intelligence, logs, and vendor feeds. Integrate that enumeration into firewalls, mail filters, and endpoint tools so matching traffic is blocked automatically. Then schedule updates, because a stale blocklist decays quickly. The risks to watch are over-blocking legitimate sources and the temptation to treat the list as complete. A blocklist is a snapshot of known threats, not a defense against unknown ones.
Parental controls are the most relatable implementation of the spectrum. A typical allowlist setup approves around 50 channels and blocks every other channel on the platform, which is the pattern the WhitelistVideo app uses. The child requests new content, and the parent approves or denies it, which keeps the default-deny posture while preserving some flexibility. Blacklist-based apps such as Bark, Qustodio, and Net Nanny take the opposite route: everything is open until something is flagged. Whitelisting suits younger children and safety-focused homes, while blacklisting tends to fit older teens who need room to explore.
Whichever model you deploy, the operational discipline is the same. Document who owns the list, how entries are added and removed, and how often the list is reviewed. An IT admin who adds an unauthenticated domain to a mail gateway allowlist creates a spoofing risk that no amount of downstream filtering will catch. Allowlist entries only help the named sender for one recipient system, while blocklist listings affect everyone who checks that list. That asymmetry is the clearest argument for treating the spectrum as a set of deliberate choices rather than a default setting.
What Are the Risks and Limitations?
Blacklists cannot defend against zero-day threats or targeted attacks, because both are unknown by definition at the moment they are used. Over-aggressive blocklist tools may also block legitimate sources that were incorrectly flagged, and the damage can be wide: SiteGround's September 2026 guidance notes that a single listing on a major blocklist like Spamhaus can degrade delivery across thousands of inboxes simultaneously. Whitelists carry their own limitations. They require strict asset and user tracking, lose flexibility as environments change, and still grant access to approved entities even if those entities are later compromised.
The asymmetry between the two models is worth restating. An allowlist entry helps exactly one named sender for one recipient system, so the blast radius of a mistake is contained. A blocklist listing affects everyone who consults that list, so the blast radius is global. That is why blocklist operators carry outsized responsibility, and why senders invest so much effort in reputation dashboards before requesting an allowlist entry. Neither model is self-sufficient, and the strongest posture usually combines a small allowlist for critical paths with a maintained blocklist for everything else, plus a review queue in between.
Which Model Should You Choose?
Choose by asset, not by habit. For systems with a small, stable set of legitimate activity and a high cost of compromise, allowlisting is the right end of the spectrum. For open environments with large and constantly changing legitimate activity, blocklisting plus monitoring is the practical starting point, with allowlisting layered onto the highest-value components. Greylisting belongs wherever the cost of an early wrong decision is high and a review step is feasible.
The YouTube scale figures make the point vividly: users upload 500 hours of video every minute, totaling 720,000 hours of new content daily. No human team can allowlist that volume, and no blocklist can enumerate it. Platforms therefore blend the models, applying automated classification, quarantine queues, and human review at different tiers. The same logic scales down to a home network or a single server. Pick the position on the spectrum that matches the volume, the value, and the cost of being wrong, then review that choice as the environment changes.
A Note on the Name Spectrum Control
The phrase spectrum control also refers to a specific company, which is worth separating from the access control concept. Spectrum Control, the RF and EMI components manufacturer, was founded in 1963 and has merged with or absorbed more than 40 companies and product lines. It reports over 70 years of experience, 20 product lines, roughly 1,100 employees, and 13 locations, according to its own corporate materials. Its April 2025 material on emission security and power EMI filters sits in the hardware domain, not the access control domain.
There is also Spectrum Controls, a separate maker of industrial automation modules supported through Rockwell Automation's TechConnect program. If you arrived here searching for either company, the relevant documentation lives on their own sites. If you arrived searching for whitelist versus blacklist spectrum control, the concept covered above is the one you want: a spectrum of access control approaches running from strict default-deny to permissive default-allow, with greylisting in the middle.
Final Takeaway
Whitelist versus blacklist spectrum control is ultimately a question of where you want to sit between default-deny and default-allow. Allowlisting is proactive, predictable, and maintenance-heavy. Blocklisting is fast to deploy, easy to run, and permanently incomplete. Greylisting buys review time in the middle. The strongest implementations do not pick one; they place each asset at the right point on the spectrum and revisit that placement as the environment, the threat landscape, and the volume of legitimate activity change.
Frequently Asked Questions
What is the difference between a whitelist and a blacklist?
A whitelist, or allowlist, defines approved entities that are permitted access, following a default-deny approach where everything is blocked unless explicitly allowed. A blacklist, or blocklist, defines prohibited entities that are denied access, following a default-allow approach where everything is permitted unless specifically blocked. They represent opposite ends of the access control spectrum.
What is a greylist and how does it differ from whitelists and blacklists?
A greylist offers a middle ground, temporarily quarantining sources that seem suspicious or unknown. Once reviewed, a source moves to either the whitelist or the blacklist. The default for greylisting is to quarantine first, which allows investigation before a final access decision is made, unlike the immediate allow or deny behavior of the other two models.
What are the pros and cons of whitelisting?
Whitelisting is very secure, blocks unknown threats by default, and reduces unauthorized access risk. However, it can be difficult to fully implement, lacks flexibility when legitimate activity changes, may hurt productivity if too restrictive, and approved entities still have access even if they are later compromised. It also requires strict asset and user tracking to stay accurate.
What are the pros and cons of blacklisting?
Blacklisting is easy to implement initially by blocking known bad actors and allows most actions by default, which keeps friction low. However, it is reactive, requires constant updates, cannot defend against unknown or zero-day threats, and a single missed entry can lead to a security breach. Over-aggressive lists can also block legitimate sources.